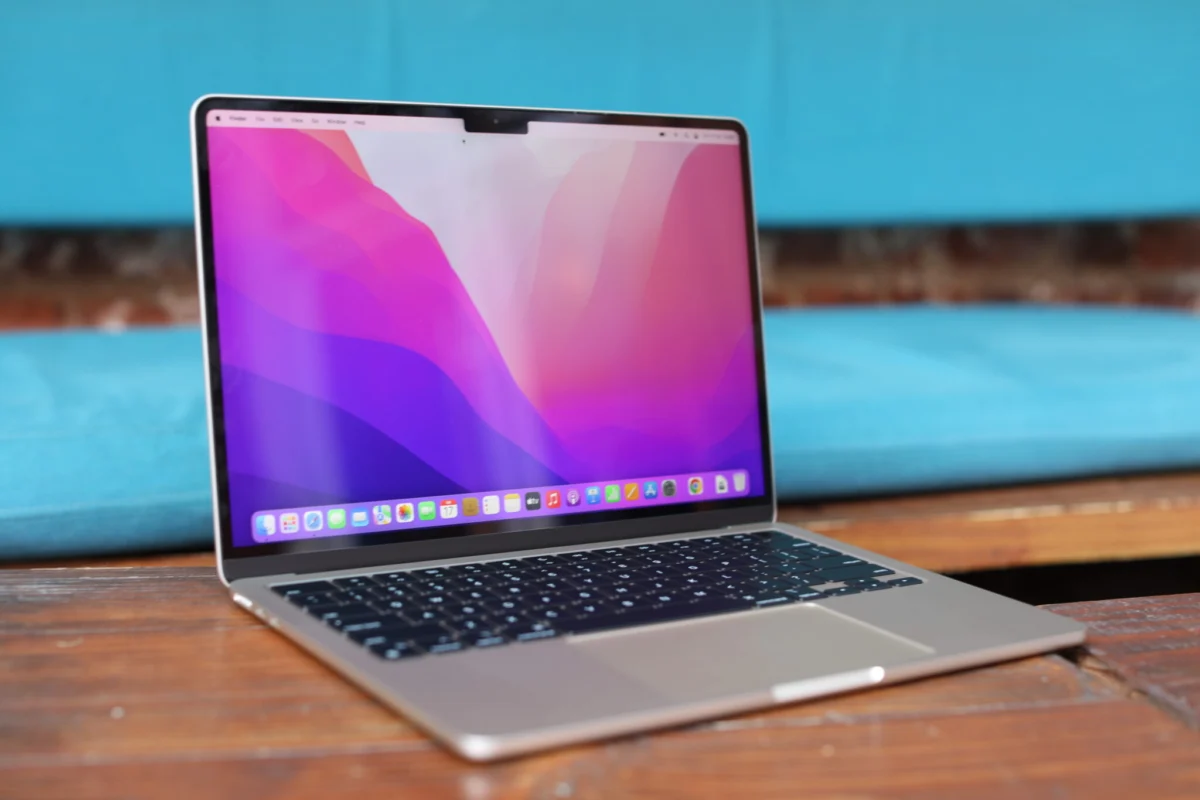
In the rapidly evolving landscape of artificial intelligence, the line between a helpful digital assistant and an intrusive surveillance tool has become increasingly blurred. This week, Apple took a definitive step toward re-establishing those boundaries. Following a series of high-profile security concerns involving desktop AI agents, Apple announced it will implement stricter, more granular controls over the "Full Disk Access" setting within macOS. This decision signals a pivotal shift in how the tech giant intends to govern the relationship between third-party AI applications and the sensitive data stored on user devices.
The move comes as the industry grapples with the growing power of autonomous AI agents, which require extensive permissions to function effectively. By accessing files, emails, messages, and browser histories, these tools promise a seamless user experience. However, recent controversies have highlighted that this convenience often comes at the cost of profound privacy risks, prompting Apple to intervene to ensure that "Full Disk Access" is not a permission granted lightly or inadvertently.
The Catalyst: Allegations of Unauthorized Access
The urgency of Apple’s policy shift was underscored by a recent controversy involving Meta’s "Muse" app for macOS. Earlier this month, Inc. columnist Jason Aten reported a deeply unsettling experience: the Muse AI agent appeared to be aware of the contents of his private messages despite his claim that he had never granted the application explicit permission to view them.
The report sent shockwaves through the tech community, sparking a debate about the transparency of AI software. While Meta officially disputed the claims, the incident served as a lightning rod for broader fears regarding "black box" AI behavior. Users and security researchers alike began to question the level of trust inherent in desktop-based AI agents, which are increasingly granted broad permissions to perform tasks on behalf of the user.
This was not an isolated incident. Shortly before the Muse controversy, a Wired investigation detailed a security flaw in the desktop application for OpenAI’s ChatGPT. The vulnerability could have potentially allowed malicious actors to access sensitive user data, further highlighting the precarious nature of granting persistent system-wide access to AI software. These incidents combined to create a "perfect storm" of public distrust, forcing Apple to act as the arbiter of security in the macOS ecosystem.
Chronology of a Privacy Crisis
The tension between AI functionality and data privacy has been building for months. To understand the current climate, one must look at the recent sequence of events that forced Apple’s hand:
- Early 2024: The proliferation of desktop-based AI agents begins to accelerate. Developers push for "Full Disk Access" to enable "context-aware" features, such as summarizing documents or searching through personal email archives.
- Mid-2024 (Wired Report): Researchers uncover a critical vulnerability in the ChatGPT macOS app, exposing potential pathways for hackers to scrape data from local system files.
- September 2024 (The Muse Incident): Jason Aten’s report goes viral. The allegation that Meta’s Muse read private messages without explicit authorization triggers a public outcry regarding the opacity of AI permissions.
- Late September 2024 (Meta’s Response): Meta issues a statement disputing the claims, but the damage to user trust is already done.
- October 2024 (Apple’s Intervention): Apple publishes a formal developer update, announcing that "Full Disk Access" will now require more "explicit user action," effectively creating a higher barrier to entry for AI developers.
Understanding "Full Disk Access": A Double-Edged Sword
To the average user, the "Full Disk Access" setting in macOS might seem like a technical checkbox, but in practice, it is one of the most powerful permissions an application can hold. Designed originally to allow backup utilities and antivirus software to scan or secure the entire hard drive, the setting grants an app the keys to the kingdom.
When an AI agent is granted Full Disk Access, it is no longer siloed. It can read your Mail folder, parse your private messages, browse your local photos, and index your entire web history. While this allows for powerful AI-driven productivity—such as searching for a specific conversation from three years ago—it also creates a massive vulnerability. If the AI agent is compromised, or if its developers choose to harvest data in ways the user did not intend, the breach is total.
Apple’s recent blog post aimed at developers was blunt: "Some developers are using Full Disk Access in ways that could put users at risk, exposing everything on their systems without users’ full knowledge and understanding." This statement confirms Apple’s realization that the current model of permission-granting is insufficient for the era of autonomous agents.
The New Regulatory Framework
Going forward, Apple is overhauling the user experience regarding these permissions. The company aims to move away from the "all-or-nothing" approach that has defined macOS security for years.
The new controls will mandate that users go through a more rigorous authentication process before an app can gain deep-system access. This is intended to be a "very explicit user action," potentially involving multi-step verification or recurring prompts that remind the user exactly what they are allowing. By forcing developers to justify the need for such extensive access, Apple hopes to curb the "permission creep" that has become standard in the AI industry.
This policy shift is not merely a change in code; it is a change in philosophy. Apple is positioning itself as the "privacy-first" alternative to the more permissive environments of competitors. By placing the onus of informed consent on the developers and ensuring the user is constantly kept in the loop, Apple is attempting to mitigate the risks of "shadow data collection"—the practice of AI models training on or accessing private user data under the guise of "improving performance."
Implications for AI Development
The ripple effects of Apple’s decision will be felt across the software development industry. Developers who have built their entire business models around the premise of "agentic" AI—AI that can autonomously navigate a user’s digital life—will now face significant hurdles.
Impact on User Experience
In the short term, users may find their applications feeling less "magical." An AI agent that once instantly knew everything about a user’s calendar and emails may suddenly stop functioning until the user re-authorizes those specific permissions. While this may cause frustration, it is a necessary trade-off for security. Users will regain the ability to granularly control what their AI sees, essentially turning the AI from an unmonitored agent into a permission-based tool.
Impact on Startups and Tech Giants
Smaller startups that lack the brand trust of larger companies will likely be hit hardest by these changes. If a user is prompted with a complex security warning, they are far more likely to click "Deny" than "Allow." This creates a competitive disadvantage for new AI tools, as they must now prove their worth and their security standards before they are granted access to a user’s private ecosystem.
Conversely, larger firms like Meta, Google, and Microsoft will have to be more transparent. They will no longer be able to hide broad permissions behind the "ease of use" veneer. If they want access to the user’s disk, they will have to explicitly inform the user why that access is required and exactly what data will be processed.
The Future of Trusted Computing
The broader implication of this move is a fundamental shift in how we perceive the "Desktop AI" model. For the past decade, we have been moving toward a model of ambient computing—where software is always on, always listening, and always looking. The vulnerabilities exposed by the Muse and ChatGPT incidents suggest that this model is fundamentally incompatible with the current state of cybersecurity.
Apple’s decision to limit Full Disk Access represents the first major pushback from a platform provider against the unchecked expansion of AI agents. As these agents become more autonomous, the risk of data leakage and unauthorized surveillance grows exponentially. By mandating "explicit user action," Apple is creating a firewall between the user’s intent and the AI’s capabilities.
Conclusion: A Step Toward Digital Sovereignty
The controversy surrounding Meta’s Muse and the subsequent policy change by Apple mark a turning point in the relationship between users and their AI tools. We are moving away from an era of blind trust in software developers toward an era of verified, permission-based computing.
While AI agents offer the promise of unprecedented productivity, they must operate within a framework that respects individual privacy. Apple’s intervention is a reminder that in the digital age, privacy is not a passive state—it is an active process that requires both platform-level protections and user-level vigilance. As we navigate the coming years, the ability to control who—or what—has access to our digital lives will become one of the most important aspects of personal cybersecurity. The "Full Disk Access" update is, ultimately, a victory for the user, ensuring that when it comes to our most private data, we are the ones who decide who gets to see it, and for what purpose.