In a rapidly shifting cybersecurity landscape defined by the proliferation of autonomous AI agents, compliance startup Comp AI has emerged as a significant player, announcing a $34 million Series A funding round this past Thursday. The round, led by Roo Capital and Grand Ventures, brings the company’s total funding to $37.5 million. This injection of capital underscores a growing investor appetite for "agentic" security platforms—tools designed not just to monitor threats, but to actively manage the complex regulatory and compliance hurdles that modern, AI-integrated enterprises face.
The Genesis: A Lesson in Failure and Focus
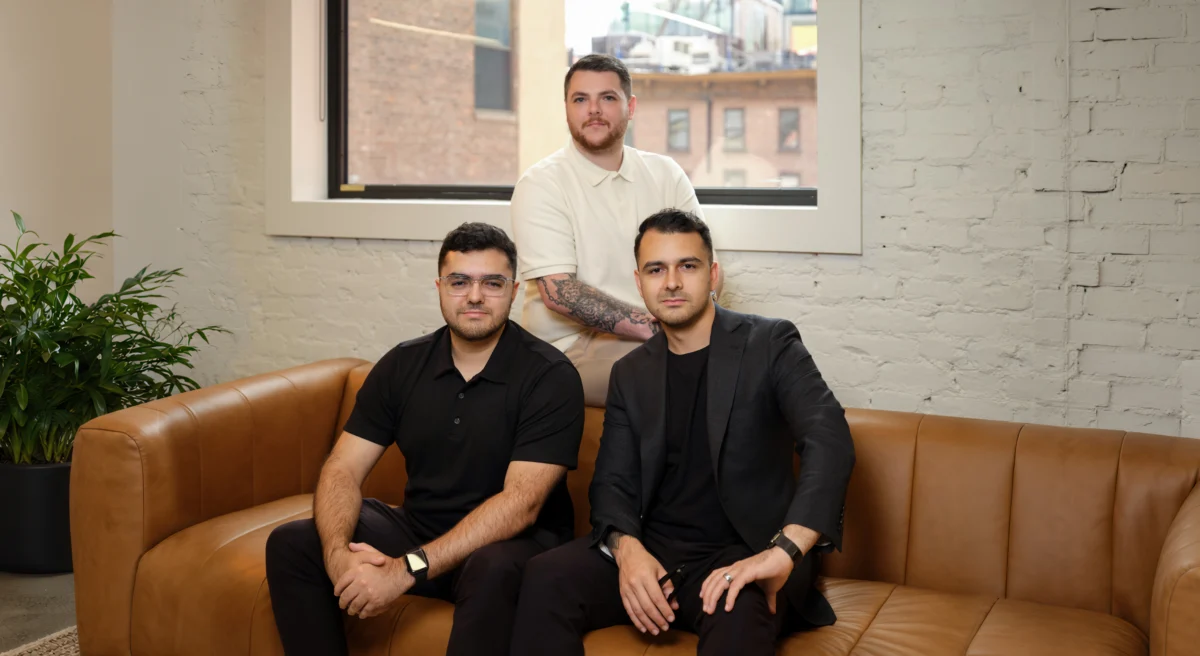
The story of Comp AI is a quintessential Silicon Valley narrative of refinement through trial and error. Founded in January 2023, the company is the brainchild of Lewis Carhart (CEO), Claudio Fuentes (COO), and Mariano Fuentes (CTO).
The trio’s professional chemistry predates Comp AI by nearly a decade. Claudio and Mariano, brothers with a long history of collaborative startup building, joined forces with Carhart a few years ago to launch LeapAI, a workflow automation platform. During that venture, Claudio served as CEO, Mariano as the senior full-stack engineer, and Carhart as head of growth.
LeapAI achieved significant traction, scaling to over a million users during its two-year lifespan. However, the founders ultimately made the difficult decision to shut the platform down. They realized that while they had built a functional tool, they had failed to establish a "sticky" enough use case to justify continued investment.
"That experience taught us everything," the team reflected. Beyond mastering the intricacies of building with Large Language Models (LLMs), they learned the absolute necessity of identifying a "hair-on-fire" problem. During their time scaling LeapAI, they encountered the brutal reality of SOC 2 compliance—a process they described as opaque, manual, and intensely distracting. "It took us a couple of months of doing things by hand," Claudio Fuentes noted. "The whole time, it meant taking our eyes off building the product."
Recognizing that many other startups were likely suffering through the same administrative quagmire, the trio pivoted. This time, they decided that Carhart would step into the CEO role to spearhead the new vision. Thus, Comp AI was born—not out of a desire to build another general-purpose AI tool, but out of a specific, painful necessity they had experienced firsthand.
Automating the Compliance Bottleneck
At its core, Comp AI is an agentic platform designed to shoulder the burden of security and compliance work. In the modern SaaS ecosystem, SOC 2 compliance is often a binary gatekeeper for revenue; if a startup cannot produce a clean audit report, enterprise customers will frequently walk away from the table.
Comp AI automates the "grunt work" of this process. Its AI agents assist in drafting company security policies, collecting evidence for audits, and—most crucially—continuously monitoring whether a company is maintaining its compliance controls.
"For a lot of software companies, security and compliance are directly tied to revenue," Carhart explained in an interview. "What Comp AI automates is much of the work companies traditionally have to do around that process."
However, the founders are quick to emphasize that they are not looking to remove the human from the loop. Instead, they view their product as a force multiplier for security teams. The platform manages the workflow, but human workers remain responsible for onboarding the AI, supporting specific controls, and providing the final seal of approval on policy drafts.
"An agent might draft a policy, for example, but a person still reviews and approves it," Carhart said. "As agents take on more consequential actions over time, we believe the level of safeguards and human approval should increase accordingly."
Expanding the Arsenal: Beyond Policy into Penetration Testing
The Series A funding will primarily fuel product expansion, a move already signaled by the inclusion of AI-powered penetration testing within their platform. This feature proactively scans a company’s codebase and infrastructure to identify vulnerabilities before they can be exploited.
By combining continuous compliance monitoring with proactive threat hunting, Comp AI is positioning itself as a comprehensive security layer. The company is part of a crowded but high-growth sector of the cybersecurity market, joining established players like Vanta and Drata. However, Comp AI distinguishes itself by focusing specifically on the unique risks posed by the "agentic era"—a time when AI agents are being granted more autonomy to access sensitive data and alter internal system permissions.
Implications: The New Security Risks of the Agentic Era
The rapid adoption of autonomous agents by enterprises has created a "security gap." Traditional compliance audits are static snapshots; they certify that a company’s security posture was sufficient at a specific point in time. In an environment where AI agents are constantly being deployed, updated, and given new access rights, that snapshot can become obsolete in days.
Carhart offers a sobering scenario: "Imagine a company completes its SOC 2 audit and two weeks later deploys a new AI agent that can access customer data, change permissions across an internal system, or introduce a new vulnerability through code deployment. The audit didn’t become invalid; it simply wasn’t designed to tell you in real time what changed afterward."
This is the void that Comp AI aims to fill. Mariano Fuentes notes that companies now need a dynamic trail of activity: what an agent accessed, what it attempted to do, and whether it remained within the strict parameters defined by the organization.
"We’re building toward a security layer that can monitor and validate those kinds of risks more continuously as these systems evolve," Mariano said. By starting with granular control over permissions and accountability, Comp AI is effectively trying to build the "governance rails" for the next generation of software development.
The Road Ahead
With $37.5 million in total funding, the Comp AI team is entering a phase of aggressive scaling. The challenge, however, will be maintaining the balance between automation and trust. As these agents gain the ability to perform increasingly sensitive tasks, the demand for transparency, auditability, and human-in-the-loop oversight will only intensify.
The founders’ background as former founders of a failed venture has clearly shaped their current philosophy. They are building with a level of pragmatism that is rare in the hype-heavy AI sector. They aren’t selling the idea of a "fully autonomous" security team; they are selling a solution to a specific, expensive, and time-consuming problem.
As the regulatory environment for AI becomes more stringent, and as corporate boards demand higher levels of visibility into how their internal AI systems are operating, platforms like Comp AI are likely to become standard infrastructure. Whether they can navigate the competitive pressures of the cybersecurity market remains to be seen, but with a clear use case and a war chest of $34 million, they have positioned themselves at the forefront of the next great evolution in enterprise security.
In the words of the founders, the era of "set it and forget it" compliance is over. In a world where software is always changing, the security and compliance that protects it must be just as agile. Comp AI is betting that the future of this space lies in agents watching agents—with a human hand on the wheel.